
Our Capabilities
Application Security Testing
SAST on every pull request and DAST against staging catch code flaws and runtime flaws before they reach production.
Software Composition Analysis
Scan open-source dependencies for known vulnerabilities and license compliance issues as they are introduced, with automated fix pull requests to support remediation.
Infrastructure as Code Security
Scan infrastructure definitions before provisioning, enforcing CIS benchmarks and identifying misconfigured access controls and unencrypted resources before deployment.
Container & Kubernetes Security
Combine container image scanning, Kubernetes admission controls, and runtime threat detection to check releases before production and govern running clusters.
MLOps & DataOps Security
Signed models, access-controlled feature stores and data lineage from source to prediction catch tampering inside the pipeline.
AIOps & Agentic Workflow Security
Agents get scoped permissions, a logged record of every tool call, and guardrails that block unsafe actions before they run.
Policy as Code & Compliance Automation
Compliance requirements run as automated pipeline gates, so audit evidence builds up continuously and isn’t assembled at review time.
Cloud Cost Governance & FinOps
Rightsizing, waste detection and budget guardrails make cloud spend something you control, not a month-end surprise.
Our Methodology
Security posture is assessed before any change is proposed. Each phase has a defined output, and controls are introduced in the order of highest impact first.
Security Posture Assessment
A technical review of the current application security landscape: pipeline architecture, existing tooling, vulnerability backlog, compliance requirements, secrets management practices, and dependency risk.
DevSecOps Architecture & Toolchain
Selection and design of the security toolchain across SAST, DAST, SCA, IaC security, container security, secrets management, and policy-as-code, mapped to the existing CI/CD pipeline with gates and thresholds defined before implementation.
Pipeline Security Integration
Implementation of the designed controls into the delivery pipeline, with the highest-impact controls rolled out first and developer enablement running in parallel so adoption is built in rather than enforced after the fact.
Continuous Security Operations
Ongoing posture monitoring, vulnerability triage and remediation support, policy updates as compliance requirements evolve, and maturity improvement against agreed targets.

Ready to scope your cloud application build?
Impact, Delivered
Automation Solutions for a Leading Healthcare Staffing Company
An end-to-end QA and test automation for a leading healthcare staffing company’s web platform and mobile application.
45%
Automation test coverage
500+
API tests
4,000+
Jira tickets validated
Automation Solutions for a Leading Healthcare Staffing Company
An end-to-end QA and test automation for a leading healthcare staffing company’s web platform and mobile application.

Secure authentication for a North American case management platform
SSI developed an Okta-integrated authentication service for a new workflow engine, enabling single sign-on and API-based authentication within the case management platform.
SSO
User authentication
Okta
Identity integration
API-based
Service connectivity
Secure authentication for a North American case management platform
SSI developed an Okta-integrated authentication service for a new workflow engine, enabling single sign-on and API-based authentication within the case management platform.

Resources
What’s new at SSI, insights, news, blogs, whitepapers, and guides from our teams.
Blog
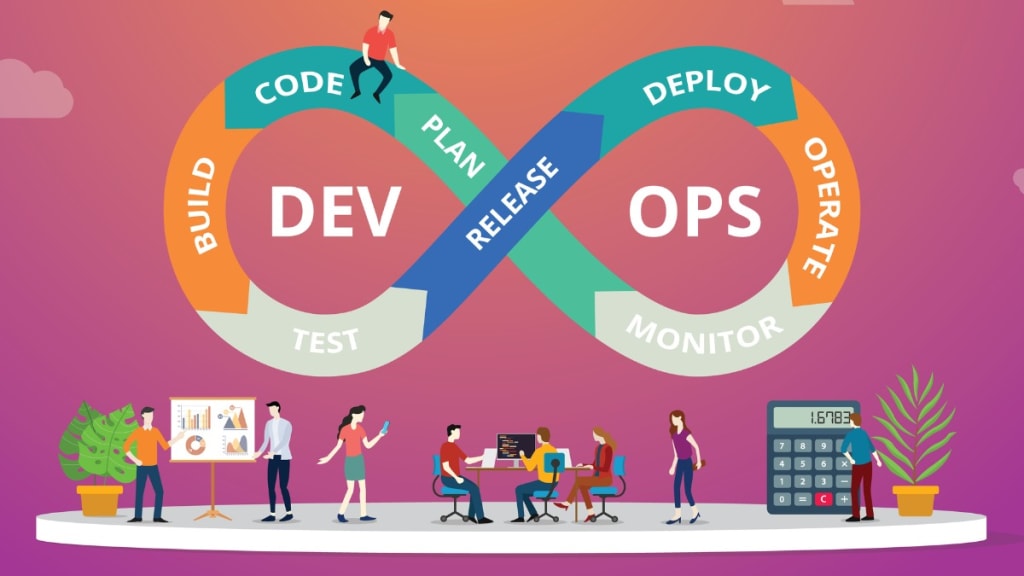
5 Ways DevSecOps Can Manage Software Supply Chains
The blog analyzes five ways how DevSecOps can manage software supply chains and minimize cyber-security risks related to open-source components
Blog
Top Best Practices and Trends for Managing DevOps in 2021
In this blog, we talk about the best practices and trends for managing DevOps in 2021
News
SSI Achieves ISO/IEC 27001:2013 Certification for Information Security Management System
The certification demonstrates that SSI has implemented, maintains, and operates an Information Security Management System which complies with the requirements of the standard ISO/IEC 27001:2013…
FAQs
Common questions before a DevSecOps engagement.
